Authentication Commands
RAPS🌼RAPSRust CLI for Autodesk Platform Services.View in glossary supports both 2-legged (client credentials🤖2-legged authServer-to-server authentication without user context.View in glossary) and 3-legged (authorization code👤3-legged authUser-authorized authentication with browser login.View in glossary) OAuth🔐OAuthIndustry-standard authorization protocol used by APS.View in glossary flows.
Commands Overview
| Command▶️CommandInstruction executed by a CLI tool.View in glossary | Description |
|---|---|
raps auth test | Test 2-legged OAuth credentials |
raps auth login | Login with 3-legged OAuth |
raps auth logout | Clear stored tokens |
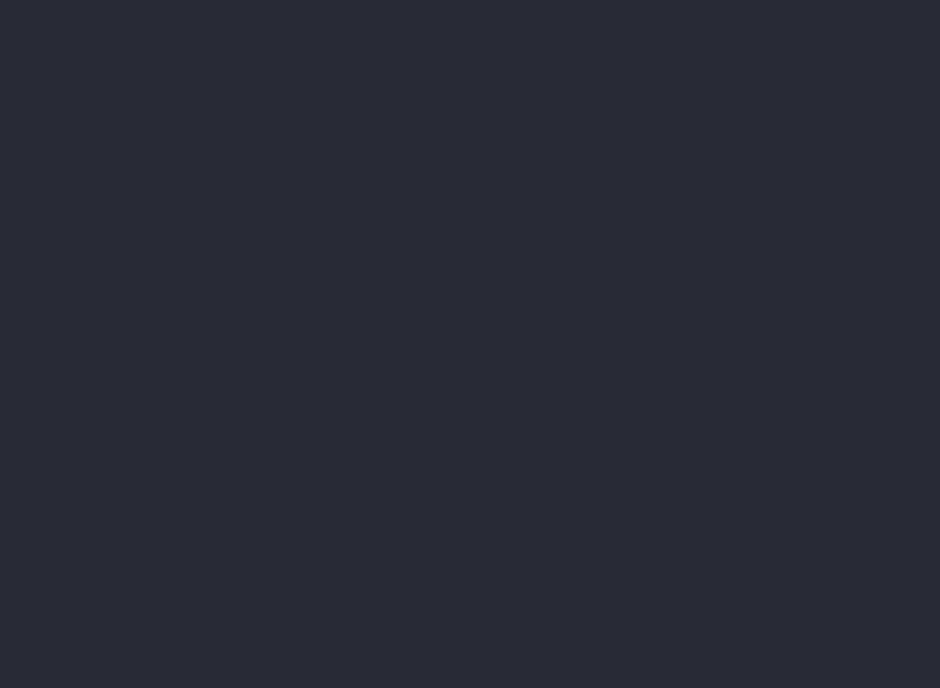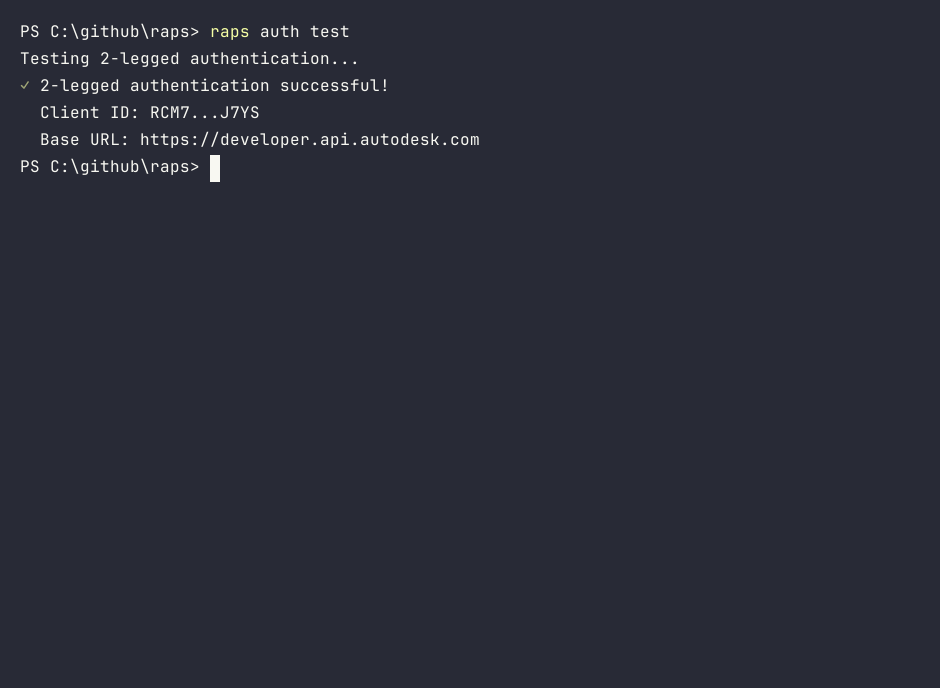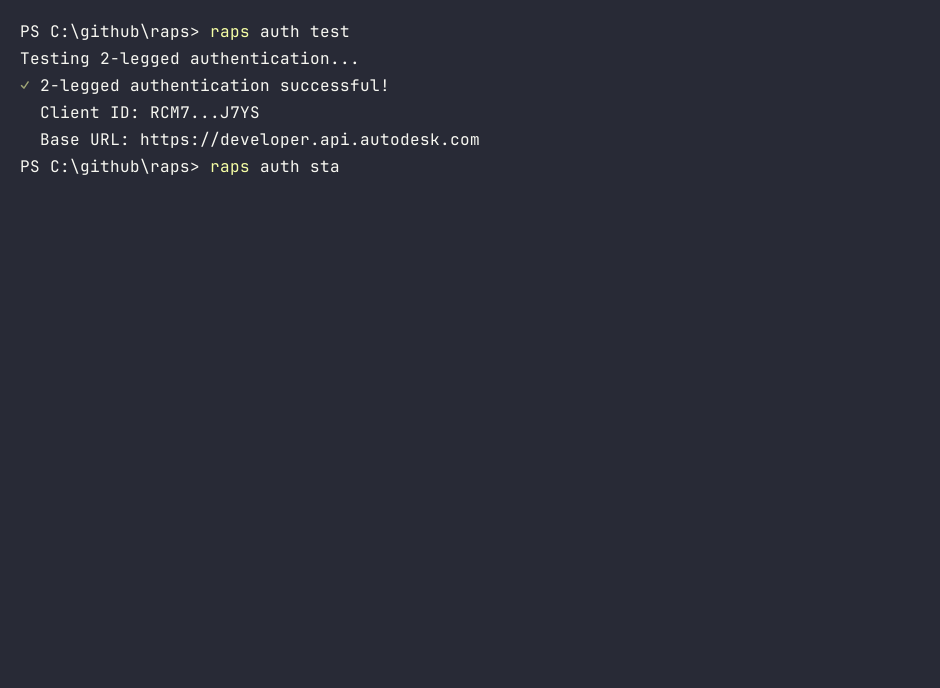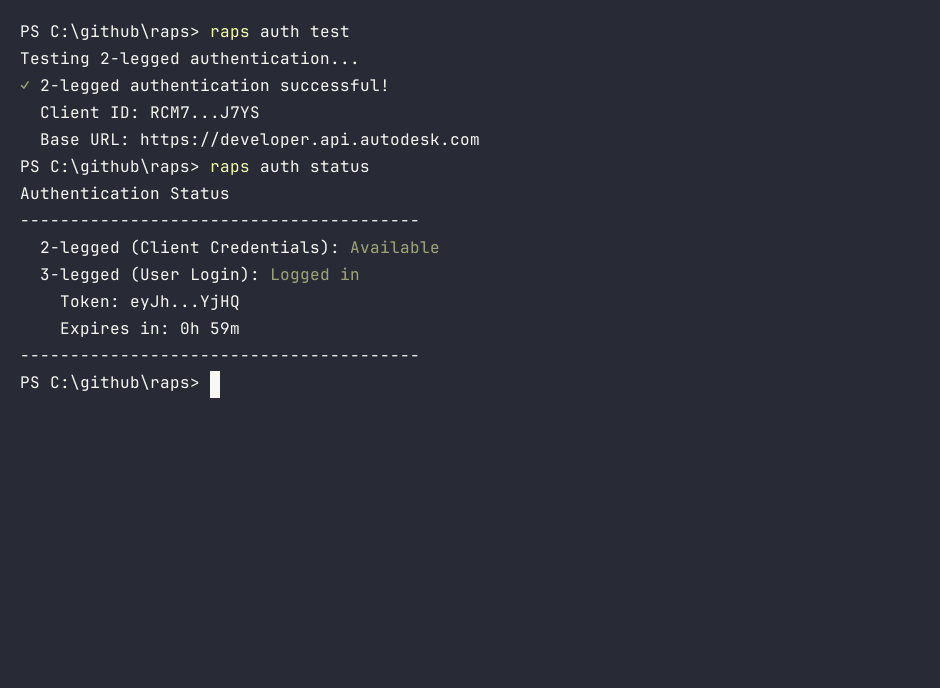
raps auth status | Show authentication status |
raps auth whoami | Show user profile👤ProfileNamed set of configuration settings.View in glossary |
raps auth inspect | Inspect token🎟️TokenCredential for API authentication.View in glossary details (scopes, expiry) |
raps auth test
Test 2-legged OAuth authentication using your Client ID and Client Secret🔒SecretEncrypted sensitive configuration value.View in glossary.
$ raps auth test
✓ Authentication successful!
  Token expires in: 3599 seconds
Requirements:
APS_CLIENT_IDenvironment variable🌍Environment VariableConfiguration value passed to applications.View in glossaryAPS_CLIENT_SECRETenvironment variable
raps auth login
Login with 3-legged OAuth. Supports multiple methods.
raps auth login [--default] [--preset PRESET] [--device] [--token <token>]Options:
-d, --default: Use default scopes without prompting-p, --preset <PRESET>: Use a preset scope collection (New in v4.6)--device: Use device code flow (for headless/server environments)--token <token>: Provide access token directly (for CI/CD🔁CI/CDAutomated build, test, and deployment pipelines.View in glossary)
Available presets:
| Preset | Scopes | Use case |
|---|---|---|
all | All 16 scopes | Full access for development |
viewer | data:read, data:search, bucket🪣BucketContainer for storing objects in OSS.View in glossary:read, account:read, user:read, viewables:read | Read-only dashboards, reporting |
editor | data:read/write/create/search, bucket:read/create/update, account:read, user:read, viewables:read | Day-to-day project📁ProjectContainer for folders and files within a hub.View in glossary work |
storage | data:read/write/create, bucket:create/read/update/delete | File uploads and OSS📦OSSAPS cloud storage for files and models.View in glossary management |
automation | code:all, data:read/write/create, bucket:read/create | Design Automation🤖Design AutomationRun Autodesk desktop apps in the cloud.View in glossary workflows |
admin | account:read/write, user:read/write, data:read | Account and user administration |
Browser-based login (default):
$ raps auth login
Opening browser for authentication...
Select scopes:
  [x] data:read
  [x] data:write
  [x] data:create
  [x] account:read
  [x] user:read
  [x] viewables:read

✓ Login successful!
  User: john.doe@example.com
Device code flow (headless): Updated in v5.1
$ raps auth login --device

Device Authorization
──────────────────────────────────────────────────
  Go to: https://rapscli.xyz/device
  Enter code: ABCD-1234
──────────────────────────────────────────────────
Waiting for authorization...
OK Authorization successful!
Open rapscli.xyz/device on any device (phone, laptop, another machine), enter the short code, and authorize with your Autodesk account. The CLI💻CLIText-based interface for running commands.View in glossary polls automatically and completes login once you approve. No local browser required — works in SSH sessions, containers, and MCP🧠MCPProtocol for AI assistant tool integration.View in glossary servers.
Preset scopes (v4.6+):
# Full access
$ raps auth login -p all

# Read-only access for dashboards
$ raps auth login -p viewer

# Design Automation workflows
$ raps auth login --preset automation
Token-based login (CI/CD):
$ raps auth login --token "eyJhbGc..." --expires-in 3600
✓ Token validated for user: user@example.com
raps auth status
Show current authentication status.
$ raps auth status
Authentication Status
────────────────────────────────────────
  2-legged (Client Credentials): ✓ Available
  3-legged (User Login): ✓ Logged in
    Token: abcd...wxyz
    Expires in: 1h 30m
raps auth inspect
Inspect the current access token for scope, expiry, and metadata.
$ raps auth inspect
Token Information:
────────────────────────────────────────────────────────────
  Valid: ✓ Yes
  Expires At: 2024-01-15 15:30:00 UTC
  Expires In: 45 minutes

  Scopes:
    • data:read
    • data:write
    • data:create
────────────────────────────────────────────────────────────
With expiry warning:
$ raps auth inspect --warn-expiry 3600
⚠ WARNING: Token expires in less than 1 hour!
Authentication Types
2-Legged OAuth (Client Credentials)
Used for server-to-server operations without user context.
Use for:
- Uploading files to OSS
- Creating buckets
- Starting translations
- Managing webhooks🪝WebhooksEvent notifications sent to your application.View in glossary
- Design Automation🤖AutomationReplacing manual processes with software.View in glossary
3-Legged OAuth (Authorization Code)
Used for operations requiring user context.
Use for:
- Accessing BIM 360🔵BIM 360Legacy Autodesk construction platform (predecessor to ACC).View in glossary/ACC🏗️ACCAutodesk's construction management platform.View in glossary hubs and projects
- Browsing folders and items
- Managing issues
- User-specific data
Token Management (v3.7.0+)
RAPS automatically:
- Stores tokens securely using OS keychain🔑KeychainSecure OS storage for credentials.View in glossary (default) or file storage
- Refreshes tokens when they expire
- Uses the appropriate token type for each operation
Secure Token Storage (Default):
- Windows: Windows Credential Manager
- macOS: macOS Keychain
- Linux: Secret Service (gnome-keyring, kwallet)
Fallback File Storage:
- Windows:
%APPDATA%\raps\tokens.json - macOS:
~/Library/Application Support/raps/tokens.json - Linux:
~/.local/share/raps/tokens.json
🔐 Security: Keychain storage encrypts tokens. File storage stores tokens in plaintext and should only be used in secure environments.
Troubleshooting
”Authentication failed” error
- Verify
APS_CLIENT_IDandAPS_CLIENT_SECRETare set correctly - Check your APS☁️APSAutodesk Platform Services - cloud APIs for CAD/BIM automation.View in glossary application is active in the Developer Portal
- Ensure credentials haven’t been rotated
”Callback URL mismatch” error
Verify APS_CALLBACK_URL matches your APS application configuration⚙️ConfigurationSettings controlling application behavior.View in glossary.
”Token expired” error
Try logging out and back in:
raps auth logout && raps auth login